Know what you expose
For finance, healthcare and other critical industries
Agentic penetration testing for your mobile app and everything behind it.
Ostorlab logs in with one-time codes and multi-factor, tests the store build with TLS pinning and obfuscation bypassed, and follows the traffic into your APIs, web back end and source code. Each AI-agent finding comes with a working exploit you can replay.
Scan a store app for free
Every release of your web app and APIs, tested the way an attacker would.
Ostorlab logs in, maps the pages and API calls behind your app, and tests access control, business logic and injection on every release.
- SSO, MFA and custom login flows, with test setup
- The REST and GraphQL APIs behind each page
- A working exploit you can replay for each confirmed finding
Add your mobile app and source code to the same scan and Ostorlab follows the path across all of them, instead of stopping at the web app. See how attack-path testing works
Catch risky code before it ships.
Connect your repositories, find vulnerable code paths and send fixes back into the pull request.
- GitHub, GitLab, Bitbucket, Azure DevOps or a standard Git server
- Risk context with affected paths, exploitability and remediation priority
- Fixes pushed into pull requests for your developers to review
Add the repository to a multi-asset scan with the APIs and apps it powers, and findings can point back to the code behind them. See how attack-path testing works
Trusted by banks, fintechs and security teams at

Attack paths
Real attacks move between assets
A token left in a repository, accepted by an API, used from a mobile app. Scan those three apart and you get three clean results, and miss the path straight through them.
Ostorlab tests your mobile app, its APIs, web back end and source code together, and proves the paths that cross them with a working exploit.
See how attack-path testing worksScanners: one asset at a time
- API docsNot tested
- API schema1 Info
- Source code1 Medium
- Mobile app2 Low
Ostorlab: one attack path
- API docsPrivileged action
transfer_funds - API schemaParameter
source_account_id - Source codeMissing
owner check - Mobile appAuth flow
otp_step_up
CriticalCross-account transfer Exploit confirmed Web back end
How it worksAgentic testing that starts
Agentic testing that starts
where scanners stop
Scanners often stop at the login screen or need an unprotected test build, and manual penetration tests take weeks per release. Ostorlab's AI agents test your app the way an attacker would, on every release, and reduce the manual testing effort you need.
- 01
Gets in
Handles login, one-time codes and multi-factor authentication, using a dedicated test phone number or TOTP seed set up with your team.
Why it matters: Most of the risk sits behind the login screen.
- 02
Gets past
Tests the build you ship to the stores, bypassing TLS pinning and obfuscation, and checks your app shielding on physical devices.
Why it matters: You test what your customers run, not only a special test build.
- 03
Goes through
Follows your app's traffic from the app into its APIs, web back end and code, and looks for business-logic flaws such as broken access checks between accounts. Web apps, APIs and source code can also be tested on their own.
Why it matters: That's where the money moves.
- 04
Proves
Backs each AI-agent finding with a working proof-of-concept exploit. When a path crosses assets, you get one replayable exploit for the whole chain, with the requests, responses and steps to reproduce it.
Why it matters: Developers fix instead of arguing.
Why teams choose Ostorlab
- Proof, not noise. Exploit-backed findings keep false positives under 5%.
- Your model, your account. Bring your own key, and the AI runs on your own model provider account, with a spend limit per scan.
- Fits your release cycle. Pipeline scans finish in under an hour, and prices are published: from $599 per app per month, billed annually.
Proof from the teams
who use Ostorlab
Results from our published case studies, and reviews from security teams on Gartner Peer Insights.

4 months → 1 week
QMC's remediation time after it added agentic security testing.
Read case study
99%
of Bumble's iOS and Android store releases scanned before going live (159 of 160).
Read case study
Every release
RSA Security runs Ostorlab SAST and DAST on each iOS and Android release as part of its formal security sign-off.
Read case study
4.8/5
Very efficient team, the support engineers are very good and knowledgeable. The product is always evolving and they take customer input very seriously.
The UI is easy to use. It took us a small amount of work to integrate the platform with our CI/CD.
The platform helped us evaluate our internal mobile applications easily and efficiently. The onborading was smooth and the UI dynamic automation is great.
Very professional and technical. Five star. I have used many similar products in the past and come across bad post sales teams. This was the opposite. Excellent delivery.
See what it finds in your app
Book a demo with our team, or start with a free scan of an app from the App Store or Google Play.
Gartner® and Peer Insights™ are trademarks of Gartner, Inc. and/or its affiliates. All rights reserved. Gartner Peer Insights content consists of the opinions of individual end users based on their own experiences, and should not be construed as statements of fact, nor do they represent the views of Gartner or its affiliates. Gartner does not endorse any vendor, product or service depicted in this content nor makes any warranties, expressed or implied, with respect to this content, about its accuracy or completeness, including any warranties of merchantability or fitness for a particular purpose
Discover your
attack surface
Ostorlab looks beyond subdomains. App stores, public registries and web crawling show every mobile app, domain and API that carries your name, so nothing ships outside your testing program.
your-company.comInternalAssetStart in minutesTest a release in minutes
Test a release in minutes
Pick an app from the store, upload a build, or point Ostorlab at a web app or API. There is nothing to install and no special test build to prepare: scans run on the build you ship, with logged-in flows set up once with your team.
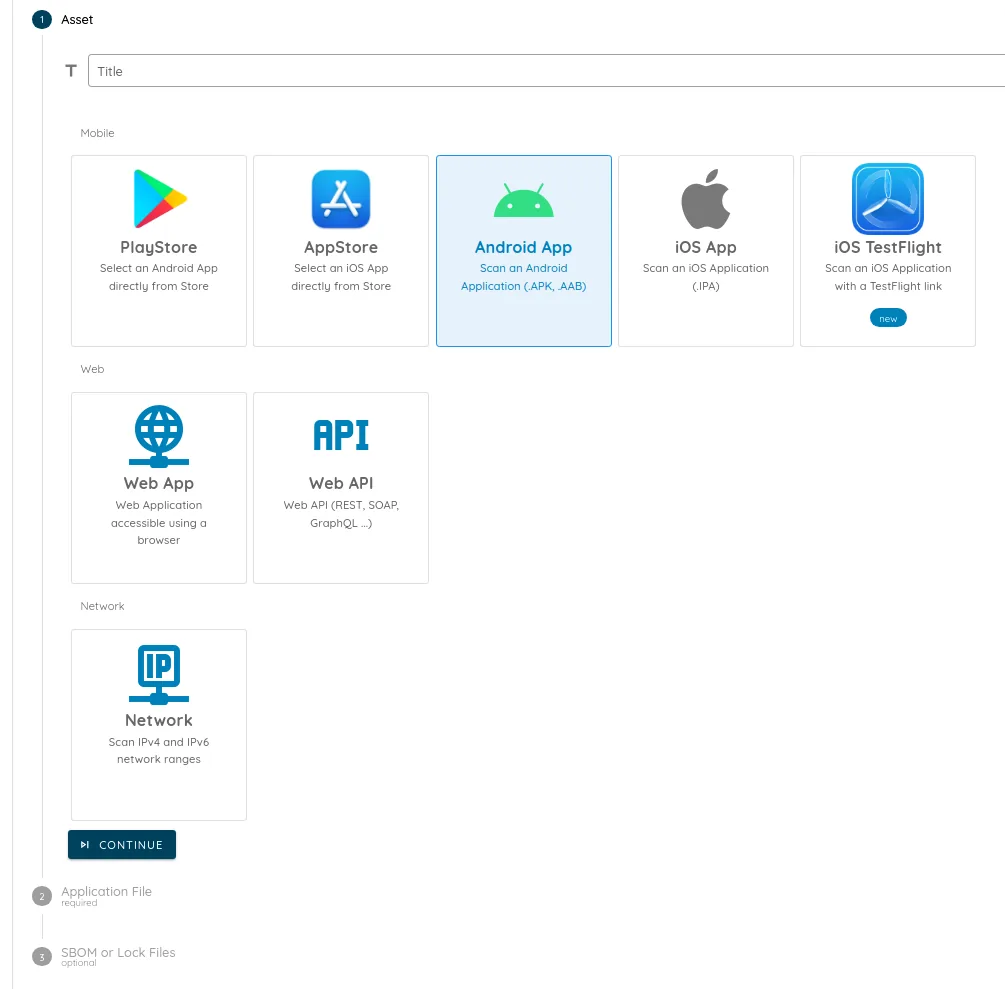

Upload .APK ^ .AAB file.Every release
Test every release automatically
Connect your store listing or CI pipeline and Ostorlab rescans each new release. Pipeline scans finish in minutes, so testing keeps pace with how often you ship.
Full Mobile scanRelease: v16.09.458See what attackers see
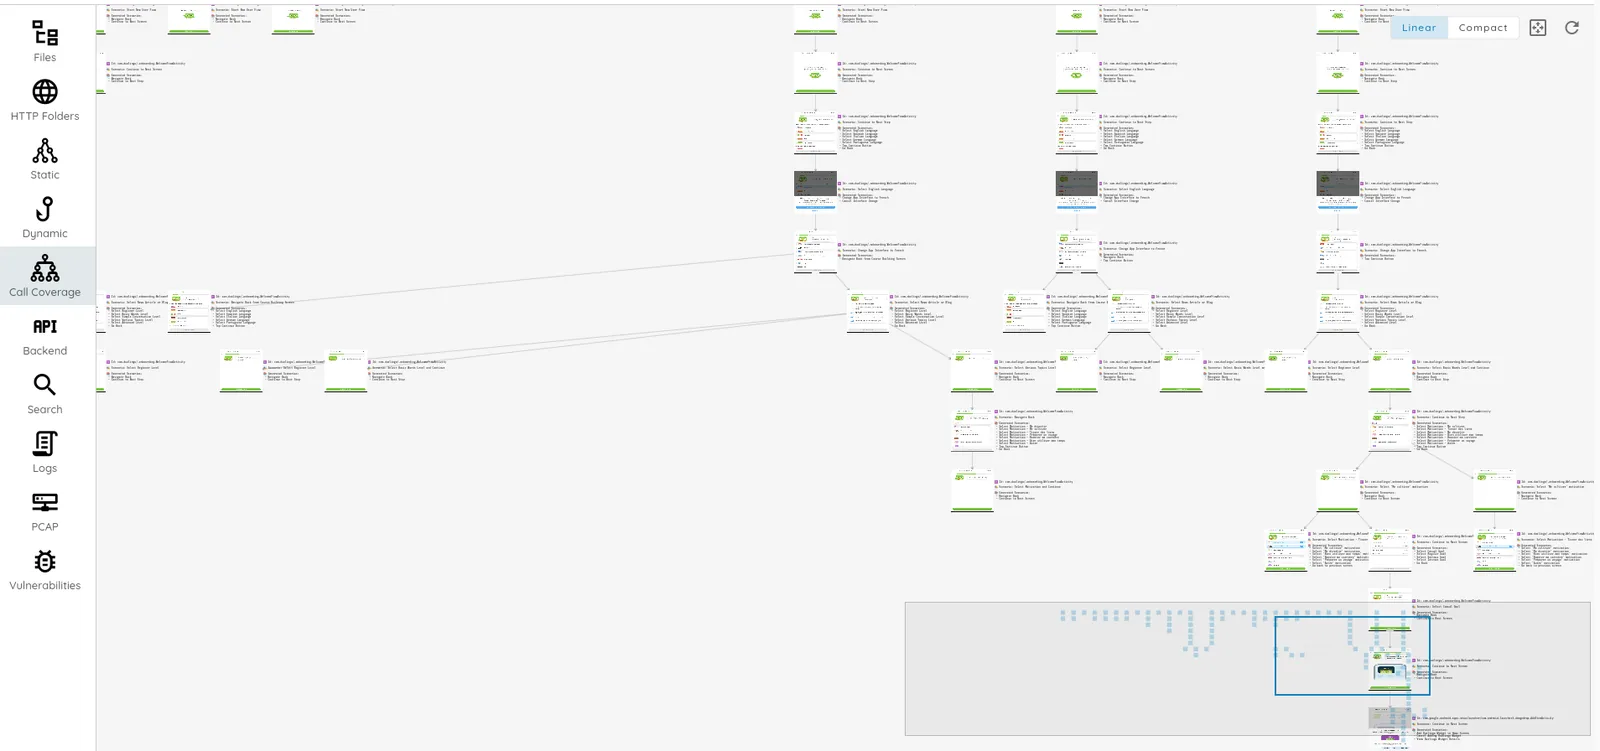
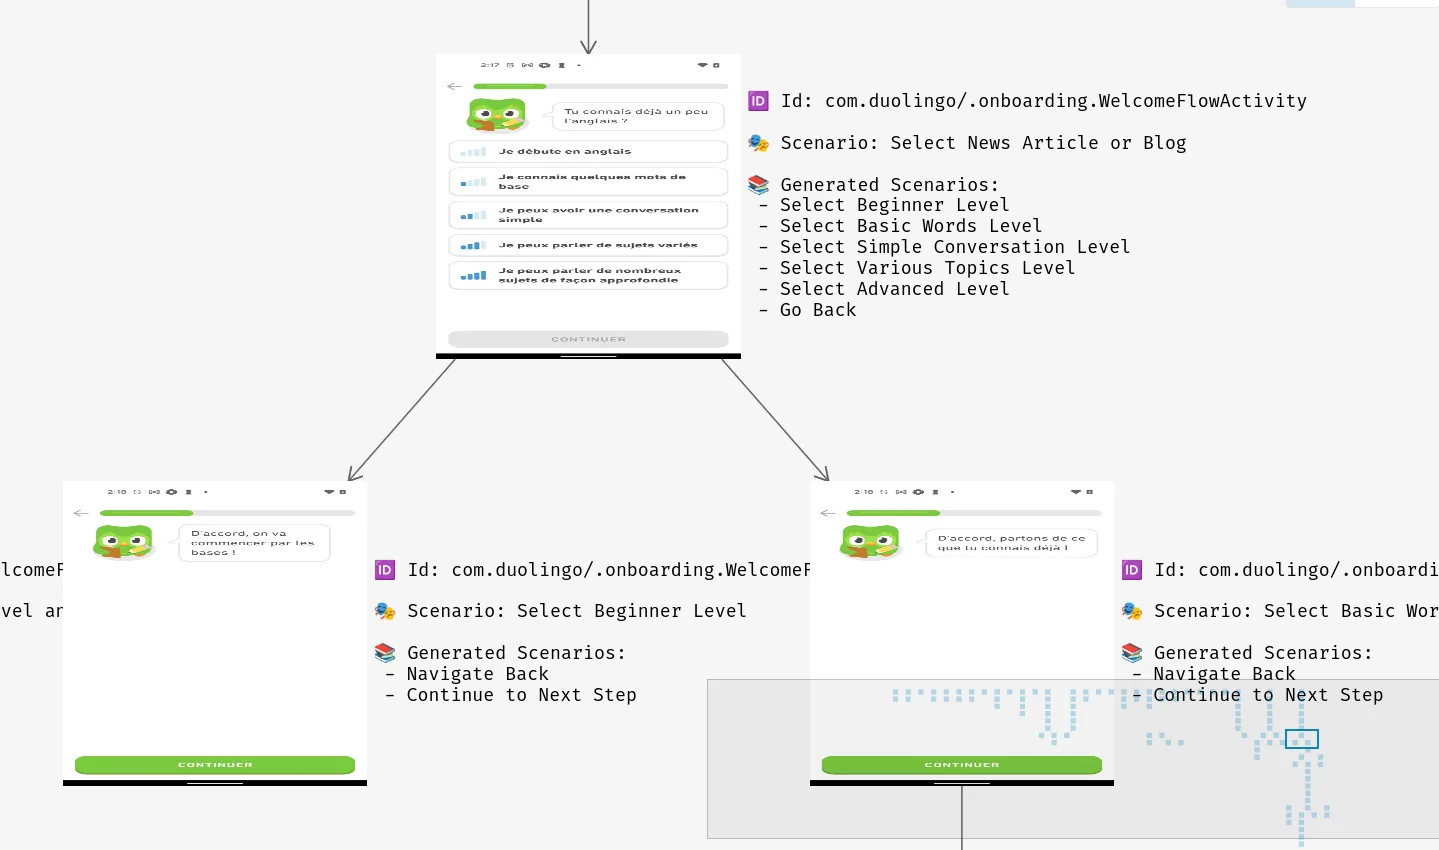
Static, dynamic and AI-agent analysis
Every finding comes with the evidence behind it: intercepted traffic, file system activity, function calls and decompiled code, all in one place. Findings from the AI agents add a working exploit you can replay.
Fix what matters
Prioritize, fix and
verify
Rank findings by business impact, send them to your ticketing tools with the context developers need, and let Ostorlab retest to confirm each fix.
Remediation > TicketStatusFix faster
Suggested code
fixes
Autofix proposes a secure code change for each finding, with the reasoning behind it. Developers review the change and apply it in one click.
Vulnerability AnalysisAI-Powered FixFits your workflow
Works with your stack
Run scans from your CI/CD pipeline, push findings to Jira, Linear or ServiceNow, sign in with SAML single sign-on, and follow app store releases automatically.

Jira

Linear

Jenkins

GitLab

GitHub

SAML

CircleCI

Bitbucket

GoCD

TeamCity

Slack
Webhook
Vanta

ServiceNow

Bitrise
Harness

Self-Hosted Git

Azure DevOps
View All Integrations
CI/CD IntegrationsGuidance for your team
Remediation guidance written for your app
Ostorlab turns a scan into a prioritized plan: what to fix first, why it matters and how to fix it, using the context you add about your app.
Scan > AI recommendationsAdd contextAccess your free community plan!
Get unlimited mobile app scans with Ostorlab, along with attack surface discovery and access to our vulnerability-tailored remediation and ticketing system.
Create an accountCurious what we've been up to ...
 Autonomous Pentesting vs. Traditional Penetration Testing: Where Agentic AI Delivers—and Where Humans Still LeadRead
 New Dashboard UI, On-Premises Scanner, Agentic Scan Knowledge, Multi-Asset Scanning, Linear & MCP Integrations, and New Model SupportRead
 Introducing Multi-Asset Deep Agentic Scan: Connected Testing Across the ApplicationRead
 Bypassing Mobile App Shielding: Where Detection Ends and Enforcement FailsRead
Trusted worldwide
Trusted by banks, fintechs and security teams
Security teams use Ostorlab's AI agents to test every release of their mobile apps, and developers get findings with a working exploit and a fix they can act on.