Comprehensive Mobile App Security Testing

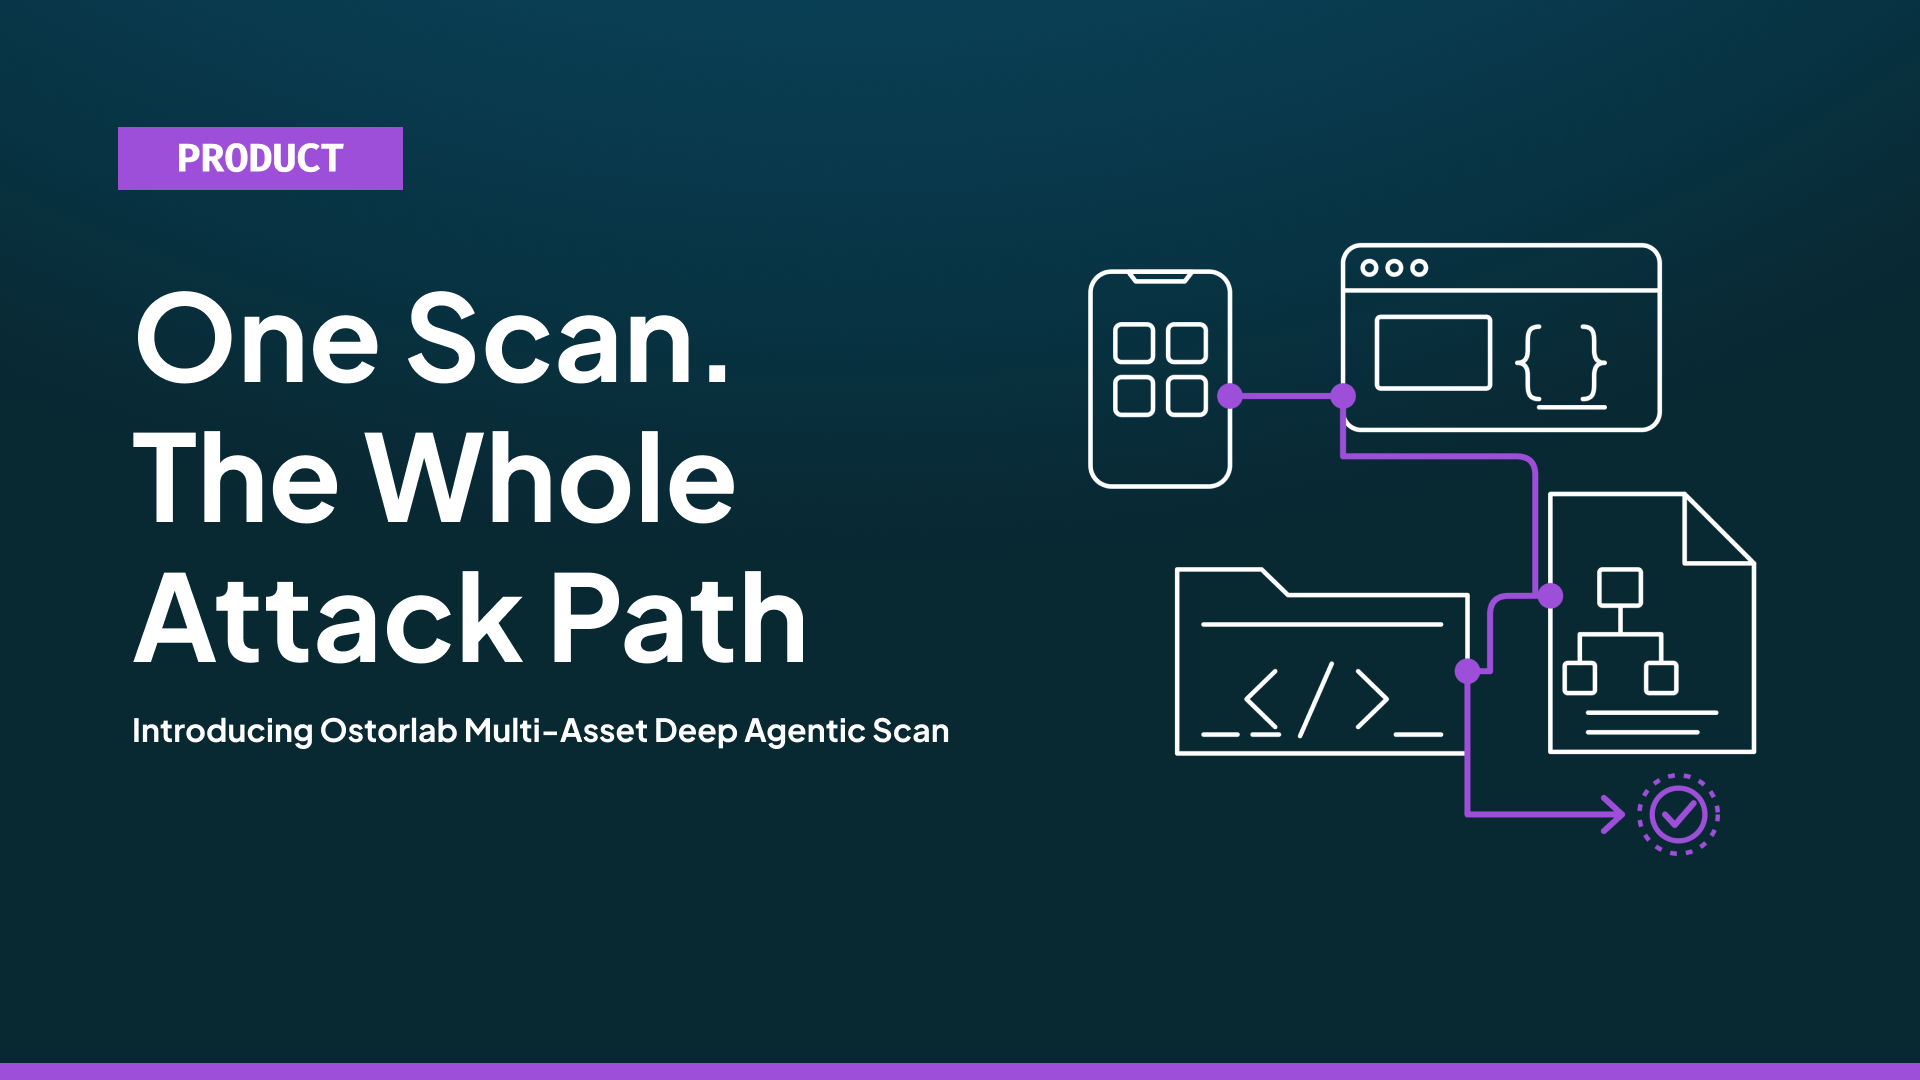
Automate mobile app security testing with static, dynamic and API analysis on every release, and go deeper with agentic penetration testing through the Agentic Deep Scan.

Easy steps to kickstart your mobile app security testing

Scan APK, AAB, IPA files or directly from Playstore, Appstore or TestFlight

Quickly and effortlessly scan APK, AAB, or IPA files, or pull apps directly from the App Store or Play Store. Streamline mobile app security testing to save time for developers and security teams, while ensuring comprehensive protection against vulnerabilities.

Comprehensive coverage for your mobile app security testing
Cover the main classes of mobile vulnerabilities with SAST, DAST, API and SCA analysis

Streamline mobile application security testing with a single platform that combines SAST, DAST, API testing and SCA. Identify and resolve issues such as injections, outdated dependencies, hardcoded secrets, weak cryptography and cleartext communication, so security and development teams can assess risk and support privacy and security compliance.

Configuration Issues
Outdated Dependencies
Hardcoded Secrets
Insecure Cryptography
Insecure Communication
...
Completely automate your mobile app security testing for seamless vulnerability detection and protection
Monitor your Apps Continuously

Experience hands-off security with Ostorlab's continuous scanning feature. Automatically trigger scans on new releases, saving you time and effort while ensuring continuous protection.

Open Web Application Security Project
National Institute of Standards and Technology
Internet of Secure Things
Achieve effortless compliance in mobile application security testing
Demonstrate your Compliance

Ostorlab helps you demonstrate compliance with industry standards like OWASP MASVS, PCI DSS, or HIPAA. It prioritizes issues to help drive customer trust and confidence.

Verify automatically the fixes of your mobile app security issues
Utilize AI-powered dynamic testing for authenticated assessments and automatic fix verification

AI-powered dynamic analysis automates app interactions and navigates both public and authenticated areas, including one-time codes (SMS, email or TOTP) once a test account is set up. Insecure behaviors are flagged during the run, and fixed issues are automatically marked as verified when later scans no longer find them. The same authenticated testing is available for web apps.

Conduct thorough analysis to push the boundaries of your mobile security testing
Rely on your mobile vulnerability scanner with confidence, but always verify its coverage for complete assurance

Access intercepted traffic, file system, function invocation, decompiled source code ... See what attackers are seeing and save hours of running tools and grouping their output.

Guidance for your team

Remediation guidance written for your app

Ostorlab turns a scan into a prioritized plan: what to fix first, why it matters and how to fix it, using the context you add about your app.

Scan > AI recommendations
Add context

Before you start

What to expect from mobile app scanning

What you get

  • Static, dynamic and backend analysis of the app, with the Full profile.
  • PDF reports: a full technical report, an executive summary, or findings mapped to standards such as OWASP MASVS.
  • With the Mobile Agentic Deep Scan, findings validated with a proof-of-concept exploit.
What you need

  • The app: from the PlayStore, AppStore or AppGallery, an uploaded APK, AAB or IPA, or TestFlight.
  • A scan profile: Fast for a quick static analysis, or Full for static, dynamic and backend analysis.
  • For logged-in areas, test credentials. One-time codes need a short setup: an SMS test number, a test mailbox or the TOTP seed.

What it covers

  • Android and iOS apps, native or built with frameworks such as Flutter, React Native, Cordova, Ionic or Xamarin.
  • Configuration issues, outdated dependencies, hardcoded secrets, insecure cryptography and insecure communication.

What it doesn't cover

  • The Fast profile is static analysis only. Dynamic and backend testing come with the Full profile.
  • Runtime protections that block tampering or instrumentation can limit dynamic analysis. Ostorlab recommends a run with protections on, then off, to compare.

What security teams say about Ostorlab

Gartner Logo

4.8/5

Read the reviews
Very efficient team, the support engineers are very good and knowledgeable. The product is always evolving and they take customer input very seriously.
Senior Appsec Engineer - Banking

Gartner® and Peer Insights™ are trademarks of Gartner, Inc. and/or its affiliates. All rights reserved. Gartner Peer Insights content consists of the opinions of individual end users based on their own experiences, and should not be construed as statements of fact, nor do they represent the views of Gartner or its affiliates. Gartner does not endorse any vendor, product or service depicted in this content nor makes any warranties, expressed or implied, with respect to this content, about its accuracy or completeness, including any warranties of merchantability or fitness for a particular purpose

Trusted worldwide

Trusted by banks, fintechs and security teams

Security teams use Ostorlab's AI agents to test every release of their mobile apps, and developers get findings with a working exploit and a fix they can act on.